AI & ML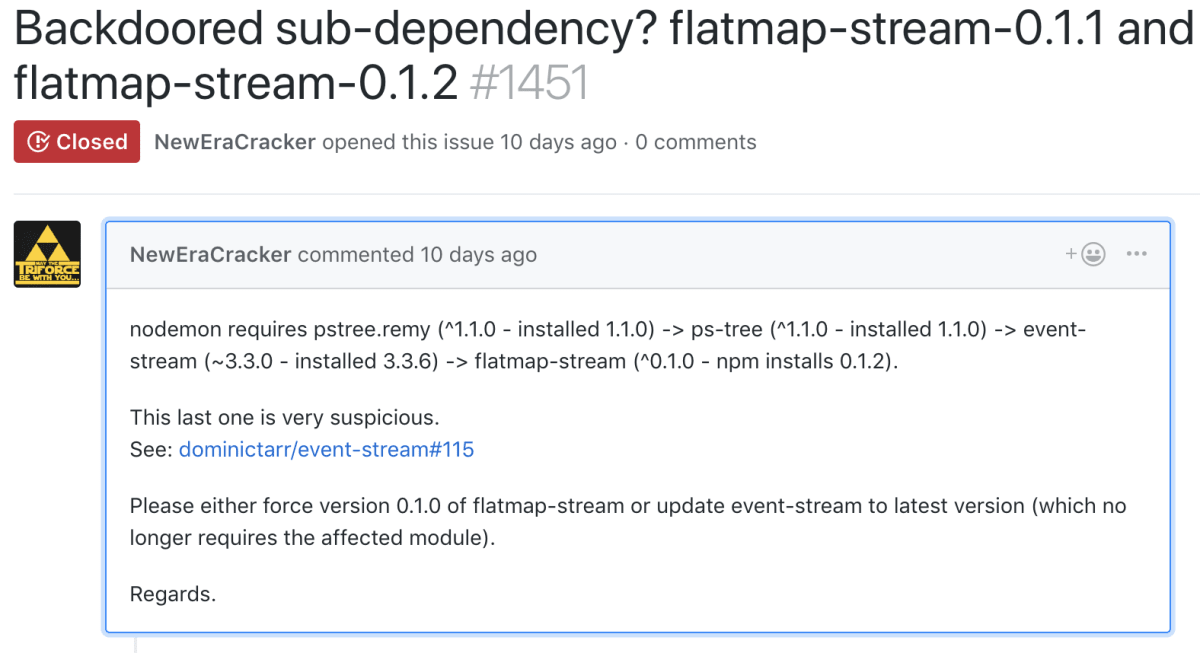
A post-mortem of the malicious event-stream backdoor
Snyk Blog0 views
A look back at the chain of events that led to the use of the malicious npm package "flatmap-stream" and a reflection on what it means for the fragility of open source.
Source:https://snyk.io/blog/a-post-mortem-of-the-malicious-event-stream-backdoor/PreviousFaster & improved tests for JavaScript lockfile based projectsNextMalicious code found in npm package event-stream downloaded 8 million times in the past 2.5 months
Related posts

I Launched My Company Website, Made Task Monitor Free, and Opened Custom Project Requests
0dev.to AI

How I turn Hacker News, GitHub and npm into product ideas every 3 hours
0dev.to AI

Lenovo's 'Encrypted' Fingerprint USB Drive Is an SD Card. How to Check Yours
0dev.to Linux

Email: OpenAI plans to merge ChatGPT's Chat and Work tabs on desktop, rolling out to select users before a wider release; Codex remains a separate experience (Ivan Mehta/TechCrunch)
0Techmeme

Memo: Alphabet is issuing €6B in euro-denominated debt across seven tranches, attracting €17B+ of demand; the company sold €9B of bonds earlier in 2026 (Reuters)
0Techmeme

S-1: Anthropic reports Q3 revenue up 12x YoY to nearly $17B, a net loss of $23.3B, up from $12.1B in Q3 2025, and operating expenses up 292% to $17.5B (Bailey Lipschultz/Bloomberg)
0Techmeme