AI & ML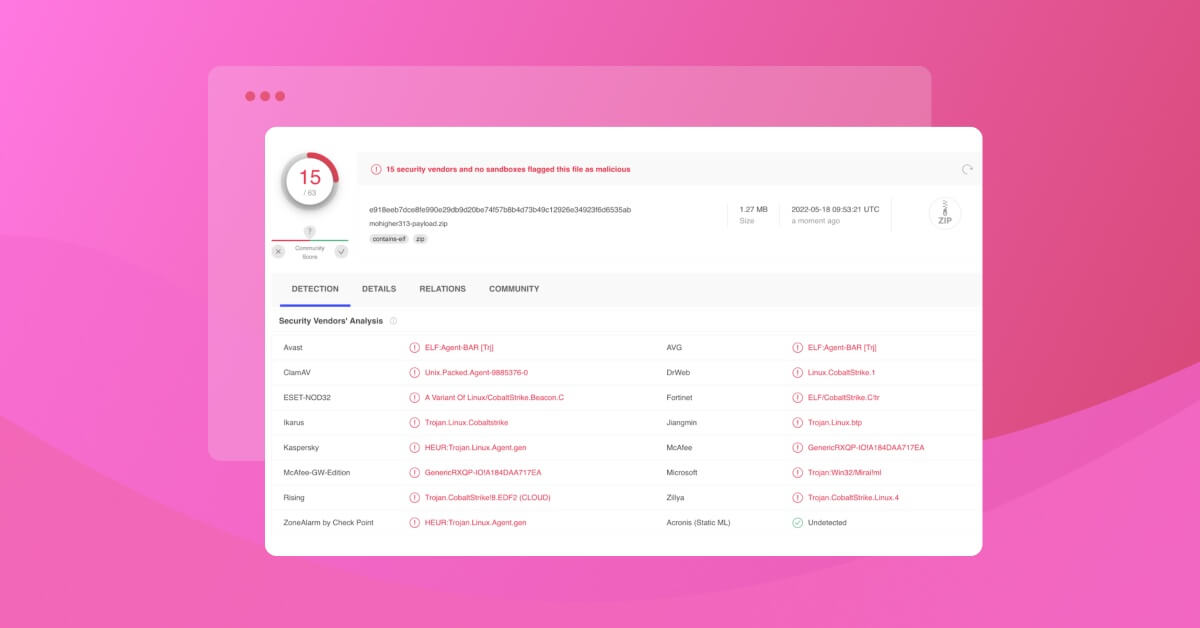
Snyk finds 200+ malicious npm packages, including Cobalt Strike dependency confusion attacks
Snyk Blog0 views
Snyk recently discovered overt 200 malicious packages in the npm registry. While we acknowledge that vulnerability fatigue is an issue for developers, this article is not about the typical case of typosquatting or random malicious package. This article shares the findings of targeted attacks aimed at businesses and corporations that Snyk was able to detect and share the insights.
Source:https://snyk.io/blog/snyk-200-malicious-npm-packages-cobalt-strike-dependency-confusion-attacks/PreviousSnykWeek Boston: Perspectives on developer security adoptionNextSnyk takes over Boston for SnykWeek
Related posts

The Download: the agentic web arrives and the drive for safer roads
0MIT Technology Review

Stop counting tokens, start counting what ships
0MIT Technology Review

OpenAI is finally merging ChatGPT’s chat and Work tabs
0TechCrunch

10 Open-Source Robotics Repositories for 3D Perception, VLA Policies, and Sensor Calibration
0dev.to

My self-modifying system tried to wire a gate-passing module into its own protection enforcer. It was refused three times.
0dev.to

Last night an AI agent performed brain surgery on a mouse
0Hacker News