Security teams can now investigate six token risks directly at the endpoint level, making it easier to prioritize findings and take action across their API estate.
APIs depend on tokens to authenticate requests and control access. But weak signing algorithms, excessive token lifetimes, exposed credentials, and inadequate expiry enforcement can undermine that protection.
Identifying these weaknesses is only the first step. Security teams also need to know which endpoints are affected, understand the associated risks, and give application owners clear guidance on remediation.
Thales’s Imperva API Security now surfaces token risk detections directly in API Inventory. Previously available in the account-level Token Risk Report, these findings are now tied to individual endpoints, bringing investigation and remediation closer together.
Why endpoint-level token risk matters
Thales’s 2026 Token & Authentication Risk Report highlights the scale of the challenge. The report found that sensitive data exposure in JWTs increased from 46.0% to 49.8% of token-risk detections year over year. It also found that the share of endpoints accepting expired tokens increased from 5.0% to 8.5%.
Nearly 40% of endpoints with token risks had two or more authentication risks, showing why teams need to understand how weaknesses can overlap.
Previously, security teams had to cross-reference the account-level report with API Inventory to locate affected endpoints. With the new enhancement, they can investigate these findings directly where they already manage API risks.
What’s new in API Inventory?
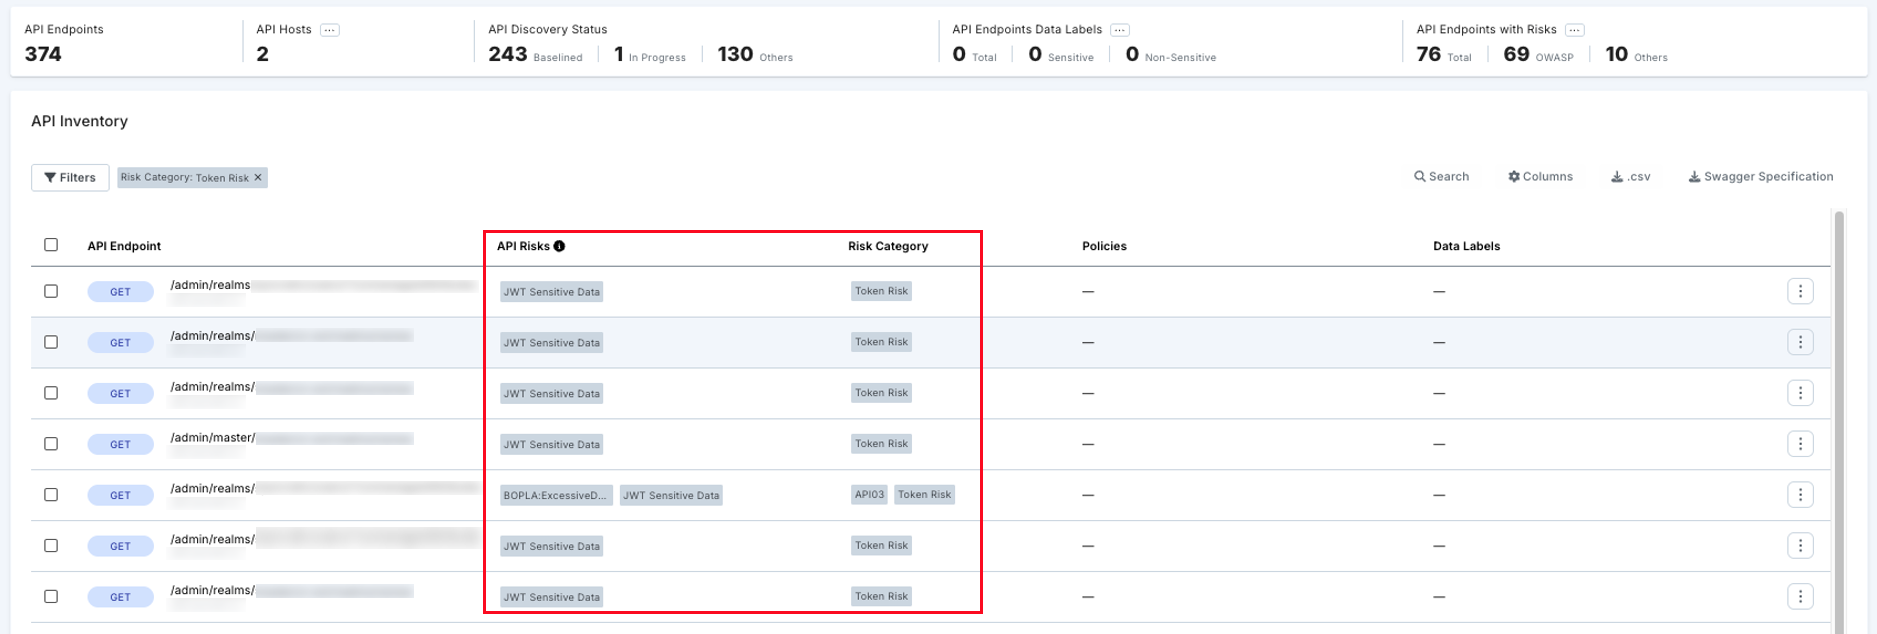
Token risks now appear as named values in the existing API Risks column, with three practical improvements.
- Filter by risk: Find endpoints associated with a specific issue, such as Expired Token Acceptance.
- Investigate at the endpoint level: Open an endpoint’s detail drawer to view the risk name, endpoint-specific description, and first and last detected dates.
- Access remediation guidance: Understand the finding and the recommended next steps without exposing the underlying tokens or credentials.
The result is a more direct workflow: identify affected endpoints, investigate the issue, and coordinate remediation without translating account-level findings into a separate endpoint list.
Six token risks. One place to investigate them.
Thales’s Imperva API Security now surfaces six token and authentication risks directly in API Inventory.
| Token risk | What it means | Why it matters |
|---|---|---|
| JWT Weak/Missing Algorithm | A JWT uses a weak signing algorithm or lacks an appropriate algorithm. | Depending on the implementation, token integrity may be undermined, potentially allowing forgery. |
| JWT Excessive TTL | A token remains valid longer than necessary. | A stolen token may remain usable for an extended period. |
| JWT Sensitive Data Exposure | Sensitive information is present in JWT claims. | JWT payloads are encoded, not inherently encrypted, and may be readable by anyone who obtains the token. |
| Auth Details in Path Params | Credentials or tokens are passed in URL path parameters. | URLs may be captured in logs, proxies, and browser history. |
| Expired Token Acceptance | An API accepts a token after its expiry. | Access may persist beyond the intended token lifetime. |
| Basic Auth Token Exposure | Reusable Basic Authentication credentials are exposed in requests. | Captured credentials may be replayed until they are changed or invalidated. |
Together, these detections help teams investigate weaknesses in token integrity, lifetime, data confidentiality, credential handling, and expiry enforcement.
From finding to fix
The enhancement turns token risk findings into a more actionable endpoint-level workflow.
- Scope the issue. Filter API Inventory by a specific token risk to identify affected endpoints.
- Prioritize. Consider endpoint exposure, data sensitivity, and other risks associated with the same endpoint.
- Route for remediation. Share the endpoint-specific description and remediation guidance with the responsible application or engineering team.
- Verify. Review subsequent detection activity after the fix is deployed. First and last detected dates provide useful context, but teams should validate remediation against relevant traffic and other available evidence.
By bringing these steps closer together, Imperva helps security teams move from identifying an authentication weakness to coordinating a response, while making it easier to investigate multiple risks affecting the same endpoint.
Securing the authentication layer behind agentic AI
As AI agents increasingly interact with business applications, internal services, and third-party systems, APIs remain a critical part of the security foundation. The Model Context Protocol (MCP) provides a standardized way for AI applications to connect with tools and external data sources, making secure authentication and credential handling important considerations for agentic workflows.
This is where endpoint-level token risk detection becomes particularly relevant.
Aligning with OWASP MCP01: Token Mismanagement & Secret Exposure
OWASP’s MCP Top 10 Identifies MCP01: Token Mismanagement & Secret Exposure as a key security risk for MCP-enabled systems.Thales’s Imperva API Security’s six token risk detections align with authentication and credential-handling concerns relevant to MCP01:
- Weak or missing JWT algorithms can undermine token integrity.
- Excessive token lifetimes can extend the window in which a compromised token remains useful.
- Sensitive data in JWT claims can expose information if a token is obtained by an unauthorized party.
- Authentication details in URL paths can increase the risk of credential exposure through logs and intermediary systems.
- Acceptance of expired tokens can indicate that token expiry is not being enforced as intended.
- Exposed Basic Authentication credentials can create opportunities for credential reuse and replay.
By surfacing these risks at the endpoint level, Imperva helps security teams investigate authentication weaknesses in APIs that support agentic workflows, where those endpoints are discovered and monitored by the platform.
This is a focused contribution to MCP security, not a claim of comprehensive MCP protection. Token risk detection alone does not discover every MCP server, prevent prompt injection, enforce least-privilege permissions, or determine whether an agent’s actions are legitimate. It provides actionable insight into an important part of the security foundation on which these systems depend.
As organizations adopt MCP and more autonomous workflows, understanding and remediating authentication weaknesses across their API estate becomes increasingly important.
Make token risks easier to act on
Security teams need more than a list of potential problems. They need to connect findings with the affected endpoints, the teams responsible, and the steps required to address them.
With six token risks now surfaced directly in Thales’s Imperva API Security’s API Inventory, teams can filter findings, investigate endpoint-specific details, and access remediation guidance in one place.
The goal is simple: make token risks easier to find, easier to understand, and easier to act on – one endpoint at a time.
Learn more: Read Imperva’s 2026 Token & Authentication Risk Report to explore the authentication risks affecting APIs today.
The post Strengthening API and MCP Security Through Token Risk Detection with Thales Imperva API Security appeared first on Blog.


