AI & ML
[$] User namespaces + file capabilities = trouble
LWN.net0 views
User namespaces are a key part of the kernel's toolkit for assembling containers; processes within a user namespace can appear to have full root access to the system while gaining no extra privileges in the wider system. At least, that is the intent. In practice, keeping privilege contained within a user namespace has often turned out to be difficult. As an example, consider this small patch series from Josef Bacik, which is intended to address some situations where a process within a user namespace can elevate the privileges of processes outside of it.
Source:https://lwn.net/Articles/1103429/Previous‘Hogwarts Legacy’ Gets a Magical NVIDIA DLSS 5 Upgrade on GeForce NOWNextCritical security vulnerability affects OpenSSH on Alpine Linux systems
Related posts
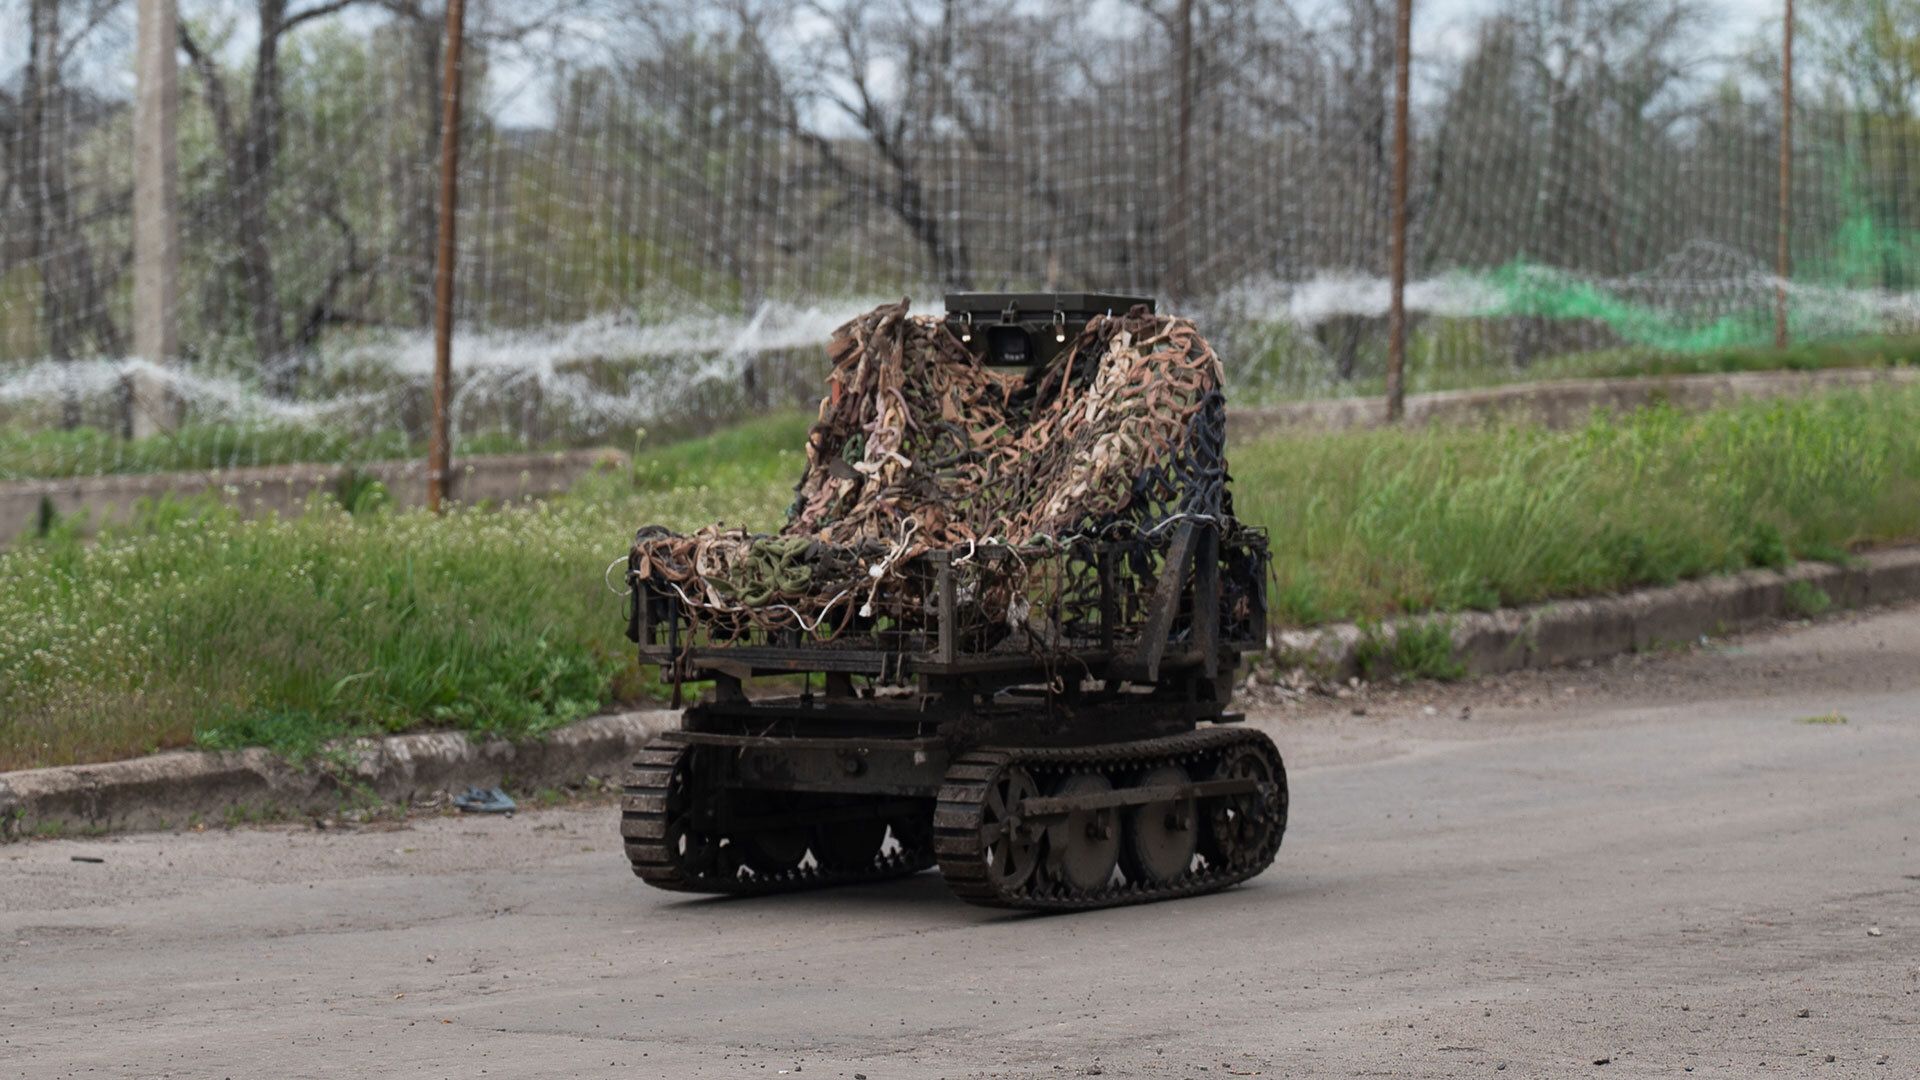
Ukraine builds combat robots to hunt Russian troops in underground gas pipelines
0Tom's Hardware

I photographed a broken clip. Claude printed a new one
0dev.to

Why a Green Build Is Not Enough for a Confident Merge
0dev.to

The EDI 812, Decoded: A Credit/Debit Adjustment Is How a Deduction Stops Being an Argument
0dev.to

DoorDash Shareholders Aren't Convinced the Company Can Take on Amazon
0Hacker News New

Show HN: Lipwise
0Hacker News New