AI & ML
[$] User namespaces + file capabilities = trouble
LWN.net0 views
User namespaces are a key part of the kernel's toolkit for assembling containers; processes within a user namespace can appear to have full root access to the system while gaining no extra privileges in the wider system. At least, that is the intent. In practice, keeping privilege contained within a user namespace has often turned out to be difficult. As an example, consider this small patch series from Josef Bacik, which is intended to address some situations where a process within a user namespace can elevate the privileges of processes outside of it.
Source:https://lwn.net/Articles/1103429/Previous‘Hogwarts Legacy’ Gets a Magical NVIDIA DLSS 5 Upgrade on GeForce NOWNextCritical security vulnerability affects OpenSSH on Alpine Linux systems
Related posts
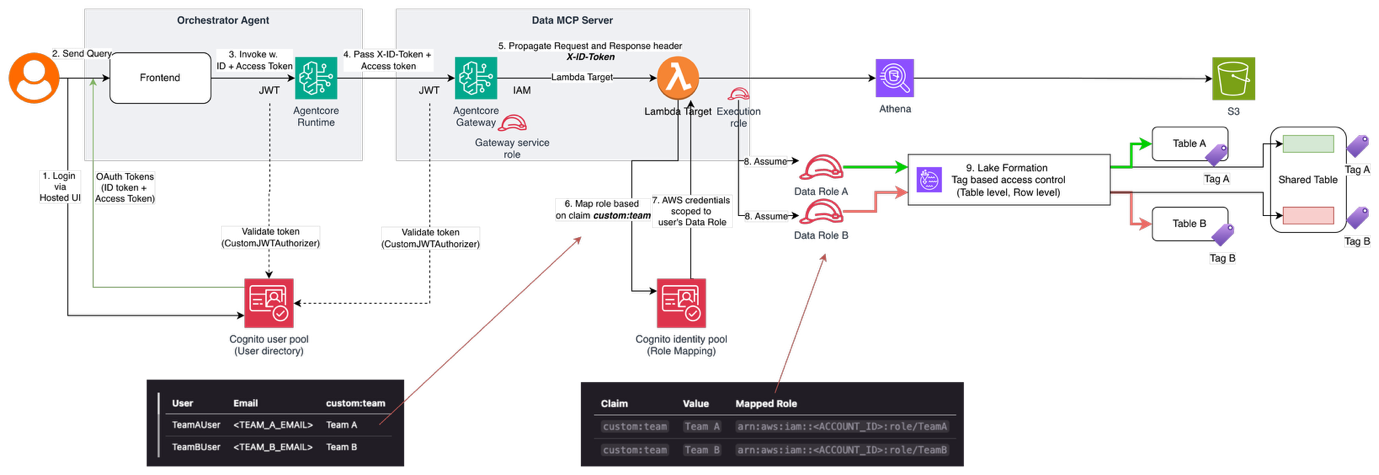
Deliver multi-tenant AI analytics at scale with AgentCore and Lake Formation
0AWS Big Data Blog

AI + Three.js: Building a Physics Playground with Compound Colliders
0dev.to AI

Your Profile Is Not a Bio Page. It Travels With Every Post You Write.
0dev.to AI

Best URL to Markdown API for AI Agents: A Live $0.001 Measurement (Nov 5, 2026)
0dev.to WebDev

I made a PDF dark mode that doesn't turn photos into negatives
0dev.to WebDev

Google cut a Gemini price in half in August. It doubles back in January.
0dev.to WebDev